No. You keep your current host and server. Traffic is routed through Sterile first and delivered to your server over a GRE tunnel.
One installer, on the server you already run
Download the installer from the dashboard and run it as root. It checks the server, brings up the GRE tunnel and registers a service so the tunnel survives a reboot. This is what it prints.
root@your-server
# ./installer.sh --install
_____________________ ______ ______ _ _______________ ______ ____ __ __
/ ___/_ __/ ____/ __ \/ _/ / / ____/ / | / / ____/_ __/ | / / __ \/ __ \/ //_/
\__ \ / / / __/ / /_/ // // / / __/ / |/ / __/ / / | | /| / / / / / /_/ / ,<
___/ // / / /___/ _, _// // /___/ /___ / /| / /___ / / | |/ |/ / /_/ / _, _/ /| |
/____//_/ /_____/_/ |_/___/_____/_____/ /_/ |_/_____/ /_/ |__/|__/\____/_/ |_/_/ |_|
https://sterile.network
[sterile] Starting sterile GRE tunnel installer for EDGE_ID=1042
==============================================================
IMPORTANT BEFORE CONTINUING
==============================================================
Before installing this tunnel, go to your dashboard:
1) Open the tunnel IP profiles section.
2) Add a TCP profile for port 22 (SSH) using one of your SSH profiles.
3) Open any other ports/profiles you need before running this installer.
If you skip this, your current SSH session can be interrupted during setup.
==============================================================
Type YES to confirm you configured profiles/ports and want to continue: YES
[sterile] Detected init system: systemd
[sterile] Configuring sysctl (persist -> /etc/sysctl.d/99-sterile-tunnel.conf)
[sterile] Applying sysctl from /etc/sysctl.d/99-sterile-tunnel.conf
[OK] Applying sysctl from /etc/sysctl.d/99-sterile-tunnel.conf
[sterile] systemd-networkd not active; skipping foreign-route persistence hardening
[sterile] Ensuring GRE kernel modules are loadable (persist -> /etc/modules-load.d/sterile_tunnel.conf)
[sterile] Loading module ip_gre
[OK] Loading module ip_gre
[sterile] Loading module ip6_gre
[OK] Loading module ip6_gre
[sterile] Ensuring route table 'sterile_1042' exists in /etc/iproute2/rt_tables
[OK] Added route table 'sterile_1042' with id 100 to /etc/iproute2/rt_tables
[sterile] Installing wrapper at /usr/local/bin/sterile_tunnel_1042.sh
[OK] Installed wrapper at /usr/local/bin/sterile_tunnel_1042.sh
[sterile] Installing systemd service /etc/systemd/system/sterile_tunnel_1042.service
[sterile] Reloading systemd units
[OK] Reloading systemd units
[sterile] Enabling and starting sterile_tunnel_1042.service
[OK] Enabling and starting sterile_tunnel_1042.service
[OK] Installation complete
[sterile] Wrapper: /usr/local/bin/sterile_tunnel_1042.sh
[sterile] Service: /etc/systemd/system/sterile_tunnel_1042.service
[sterile] Log : /var/log/sterile_tunnel_1042.log
# ./installer.sh --status
_____________________ ______ ______ _ _______________ ______ ____ __ __
/ ___/_ __/ ____/ __ \/ _/ / / ____/ / | / / ____/_ __/ | / / __ \/ __ \/ //_/
\__ \ / / / __/ / /_/ // // / / __/ / |/ / __/ / / | | /| / / / / / /_/ / ,<
___/ // / / /___/ _, _// // /___/ /___ / /| / /___ / / | |/ |/ / /_/ / _, _/ /| |
/____//_/ /_____/_/ |_/___/_____/_____/ /_/ |_/_____/ /_/ |__/|__/\____/_/ |_/_/ |_|
https://sterile.network
SERVICE NAME : sterile_tunnel_1042
WRAPPER PATH : /usr/local/bin/sterile_tunnel_1042.sh
LOG PATH : /var/log/sterile_tunnel_1042.log
META PATH : /var/lib/sterile_tunnel/1042.meta
SYSCTL CONF : /etc/sysctl.d/99-sterile-tunnel.conf
RT TABLE : sterile_1042 (100)
Tunnel : gre_1042
State : UP
MTU : 1476
Local : 203.0.113.10
Remote : 82.41.156.1
GRE TTL : 255
Assigned IPv4s : 82.41.156.24/32
Assigned IPv6s : -
---- traffic ----
RX : 1.2 MiB (9412 pkts)
TX : 3.8 MiB (11207 pkts)
RX errs : 0
TX errs : 0
INIT SYSTEM : systemd
What you need
- Root access on a Linux server
- A kernel that can load the ip_gre module
- Your SSH port added to a profile in the dashboard first, or the install can cut your session
Your host's protection and Sterile
| Typical host protection | Sterile | |
|---|---|---|
| When an attack is too large | Your IP is null-routed | The attack is filtered |
| Your server's address | Public | Hidden behind a Sterile IP |
| When filtering starts | After detection | Always on |
Watch it from the dashboard
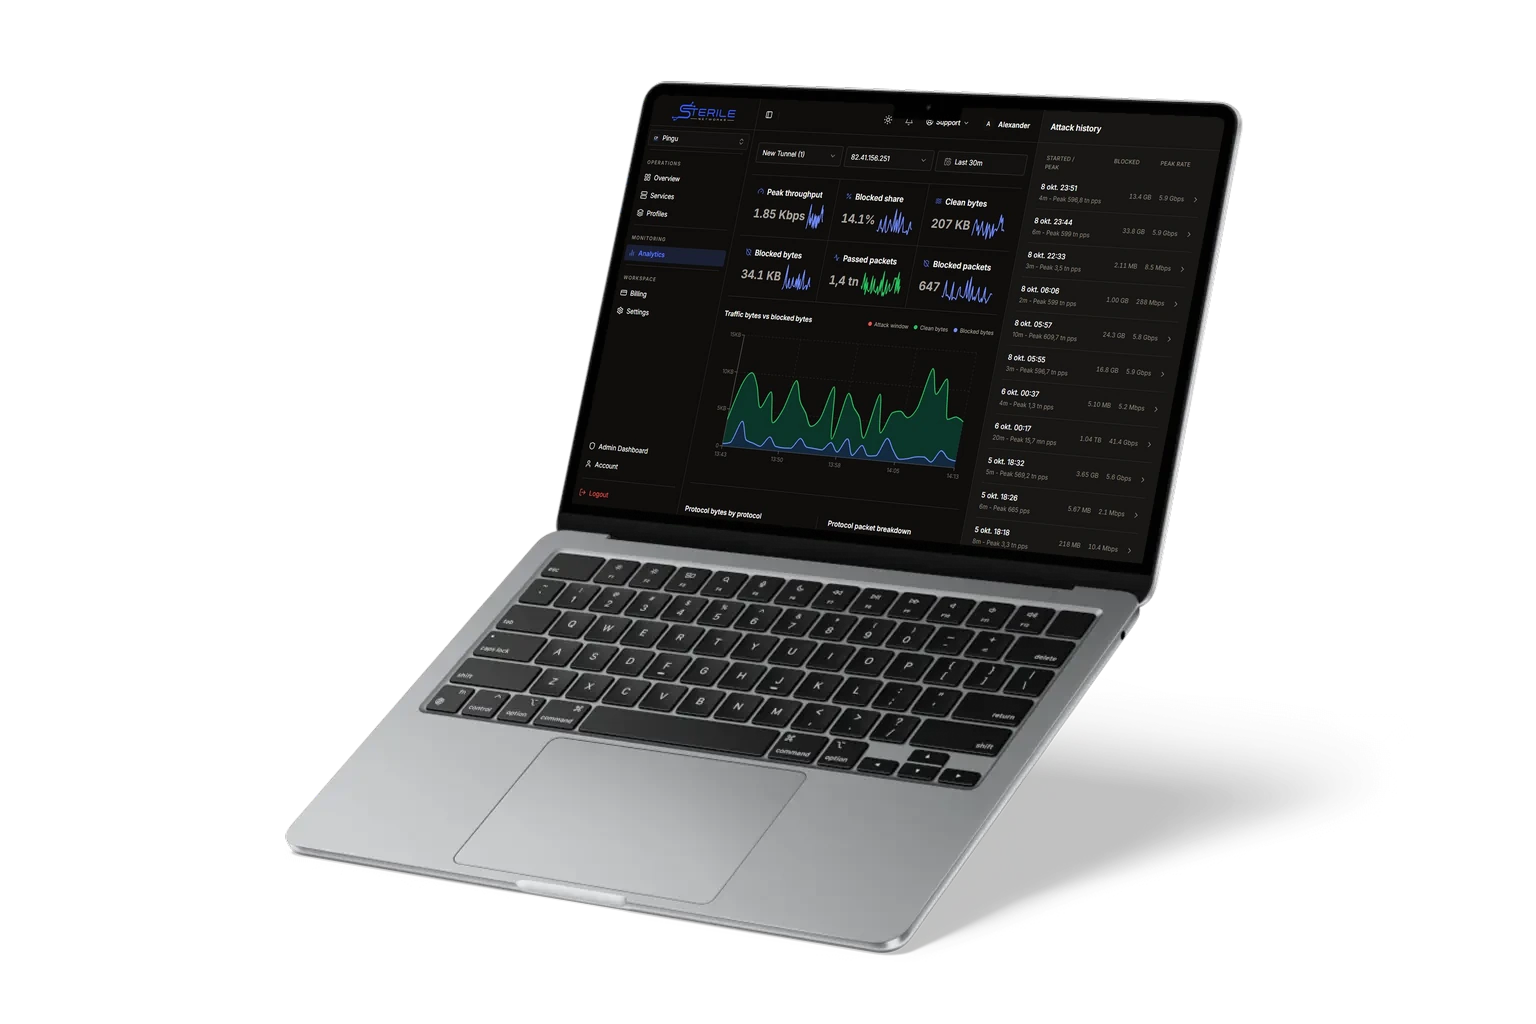
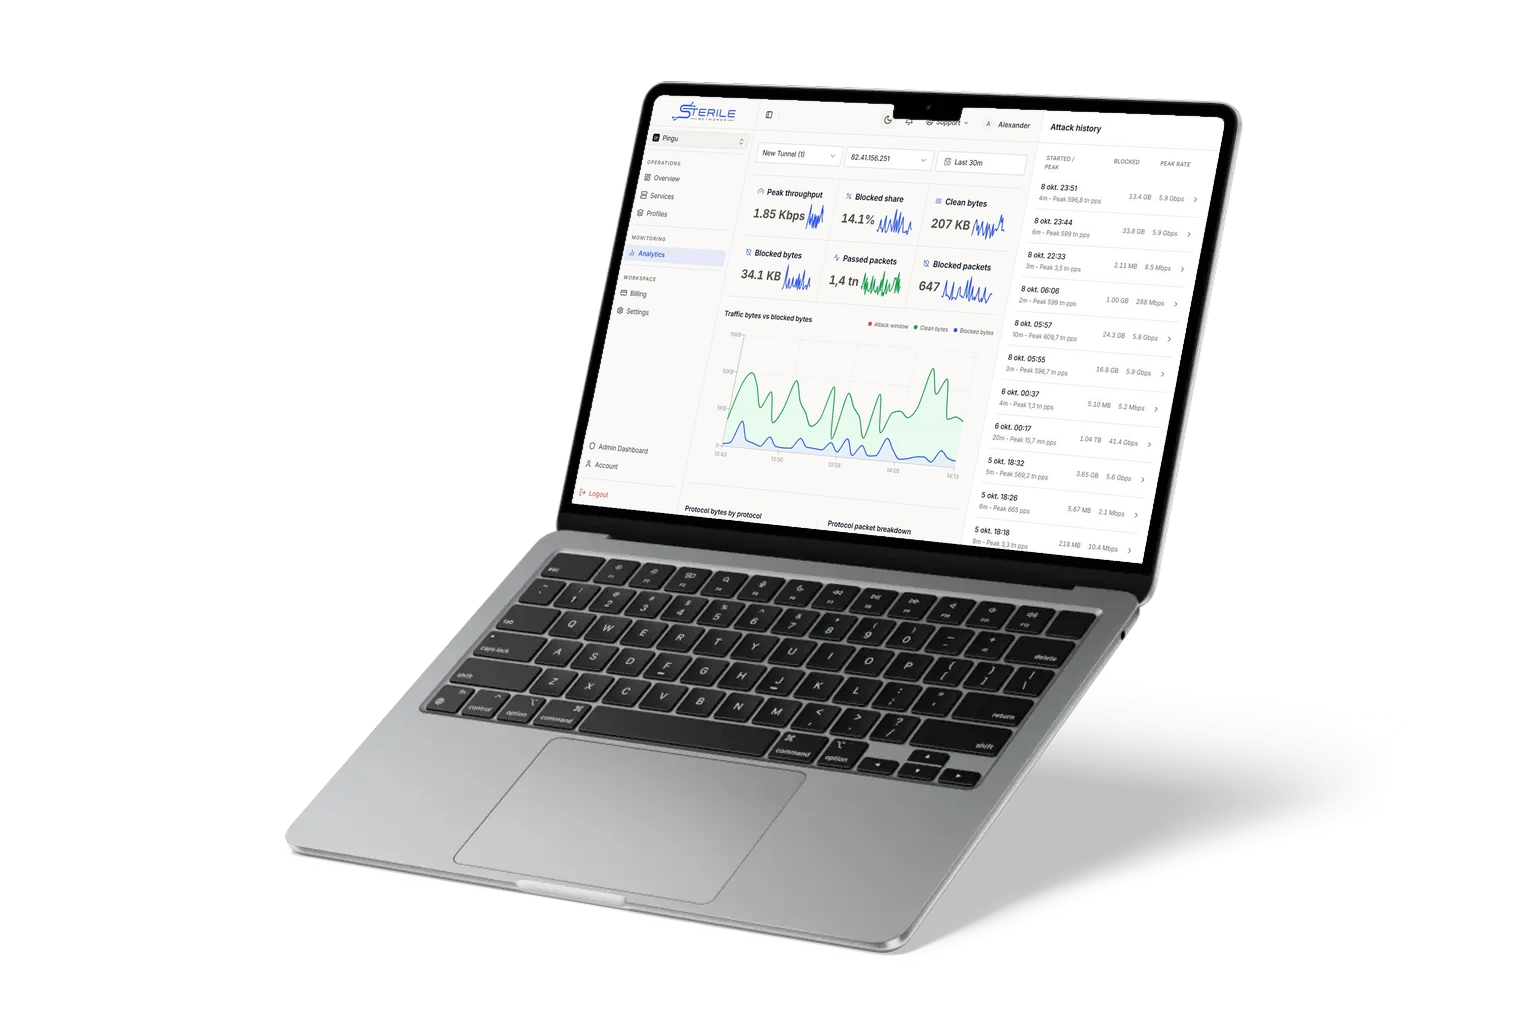
Clean traffic, blocked traffic and every attack on your server, as it happens.
Built for a single server
- Works with your current host
- You keep your provider, your server and your setup. The only requirement is that the server can run a GRE tunnel.
- VPS or dedicated
- The same protection covers a small VPS and a large dedicated server. You size it by traffic, not by hardware.
- Always-on filtering
- Mitigation runs continuously, so there is no detection delay to sit through when an attack starts.
- Hidden origin
- Your server's real address stays out of public view. Only clean traffic from our edge reaches it.
- Filtering you can tune
- Start from a premade profile and adjust the rules for your ports and traffic.
- Live analytics
- See clean traffic, blocked traffic and attack history for your server in the dashboard.
Questions about protecting a server
What people ask before putting a VPS or dedicated server behind DDoS protection.
Yes, as long as the server can run a GRE tunnel. Some container-based VPS plans do not allow that, so check with your host if you are unsure.
Host protection is often built to protect the host's network. When an attack is larger than it handles, the usual response is to null-route your IP, which takes you offline. Sterile filters the attack instead, so your server keeps answering.
A little, because traffic takes one extra hop through our edge. How much depends on the distance between your users, our edge and your server. Read the latency guide
You choose the reserved speed, clean traffic and protected IPs you need, and pay monthly for that. View pricing
Keep your server online
Add protection to the server you already run, and be filtered before the next attack arrives.